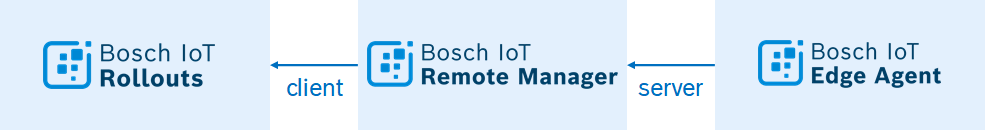
The integration with Bosch IoT Rollouts means that multiple Bosch IoT Remote Manager instances can be connected to it, so we will need one Rollouts certificate, which can be self-signed, or can be signed by a Certificate Authority. This Rollouts certificate will then act as a Certificate Authority, which signs different Remote Manager certificates, for different Remote Manager instances.
The same principle applies to Remote Manager and devices running Bosch IoT Edge. Remote Manager's certificate will act as a Certificate Authority, and will sign different certificates for different devices.
Remote Manager uses only certificate authentication to Rollouts and Edge. The reason is that if we allow basic and certificate authentication, in case of a global configuration (applying to all devices) - changing from one to another certificate will result in re-configuration of devices, which is not acceptable. This leaves us with the only option to make the authentication mode per device. But this mode requires a lot of manual work, a lot of generated certificates/passwords which will make the product much harder to use. The same is valid for Rollouts since there will be multiple Remote Manager instances connected to it. That is why the best possible approach is to use certificates only.
This section includes the following guides: