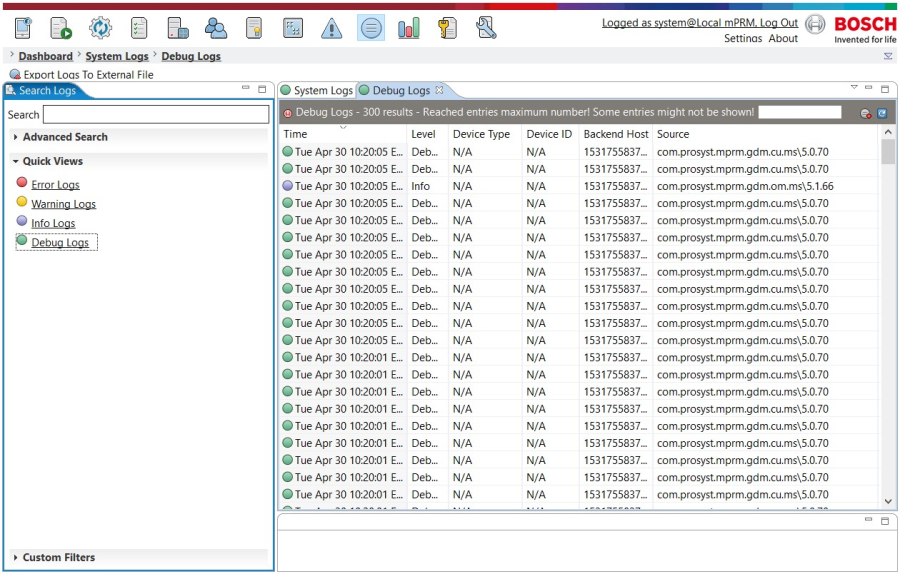
The System Logs node of the console allows you to view the system logs. Logs are short messages about various events occurred while RM functions e.g. failure of management task, runtime performance of modules or any specific information that log entry creators consider important.
General Description
Logs can be retrieved and viewed through the System Logs view of the console dashboard - click the  button from the toolbar at the top of the console or go to Dashboard -> System Logs.
The Logs navigation area view has expandable sections - Quick Views, Advanced Search and Custom Filters. The Quick Views section offers shortcuts to error, warning, info and debug logs. The Advanced Search allows you to filter the logs by specific criteria, and then save the filter and apply it again from the Custom Filters section.
The logs that satisfy the selected conditions from the expandable sections appear on the right, sorted by: time of occurrence, level, device type, device ID, backend host and source.
The icons generally used to describe logs levels are:
-
 - Represents error logs - related to runtime performance of modules.
-
 - Represents warning logs - when a human intervention is needed to fix the system dysfunction.
-
 - Represents system info logs - e.g. logging/registering a new OSGi device, start bundles etc.
-
 - Debug logs - all the system self debugging logs
Log Details
The following properties for a selected log appear when selected particular log from the list:
- Time - Contains the exact date and time of the event that triggered the log.
- Level - Indicates the error level (Error, Info, System, Warning).
- Source - The concrete bundle or package which triggered the log generation.
- Device Type -
- Device ID - Contains the ID of the managed device for which the log is generated.
- Backend Host - Contains the ID of the host originating the log.
- Message - Contains the message describing the alert. It has a pop-up menu that allows you to copy the text.
Filtering Logs
If you want to view logs filtered by certain criteria, go to the System Logs dashboard view and use the filter options provided in the Advanced Search expandable section: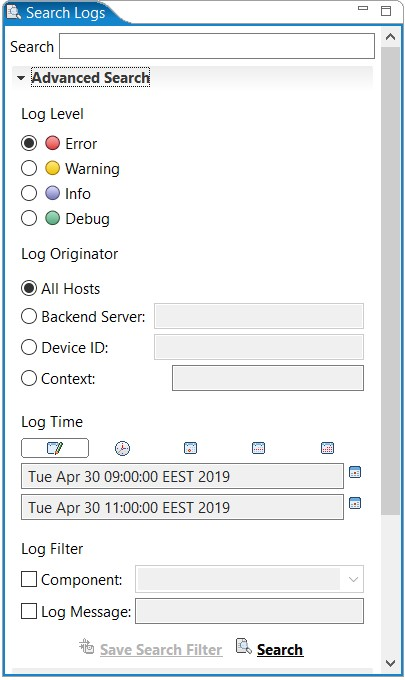
1. Specify the Advanced Search options attributes:
- Log Level - specify which kind of system logs to display
- Log Originator - specify the source of logs to retrieve
- Log Time - enter the time frame (start and end date) for which the logs should be obtained
- Log Filter - filter the log by: Component (choose from the drop down menu the system component which logs to retrieve) and Log Message (if you want to explicitly see log containing cerating message like "Error while calling back ManagedService")
2. Finally, click the Search action to apply the filter.
Saving a Filter for Further Use
The RM Console gives you the option to save a filter and then apply it again on generated logs, saving you the efforts in defining complex search criteria again and again. To save a filter:
- Define the filter attributes in the Advanced Search section as described in "Filtering Logs" above.
- Apply the filter by selecting the Search action.
- Once the search is complete and results displayed, click the Save Search Filter action.
- Name the search filter and click OK.
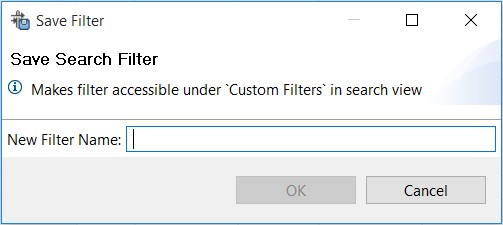
The filter will be added to the Custom Filters expandable section. To apply it, simply click on it.
A saved filter:
Exporting Alerts to a CSV File
You can save specific logs exported to a CSV file. Next, the file can be opened in a spreadsheet management application and explored in detail.
To export log data to a file:
- Click the Export Logs to External File action from the administrative toolbar at the top. An export wizard appears.
- In the Logs to Export step, specify the attributes of the logs that should be exported. The filter options are similar to the ones in the Advanced Search section. Click Next to proceed.
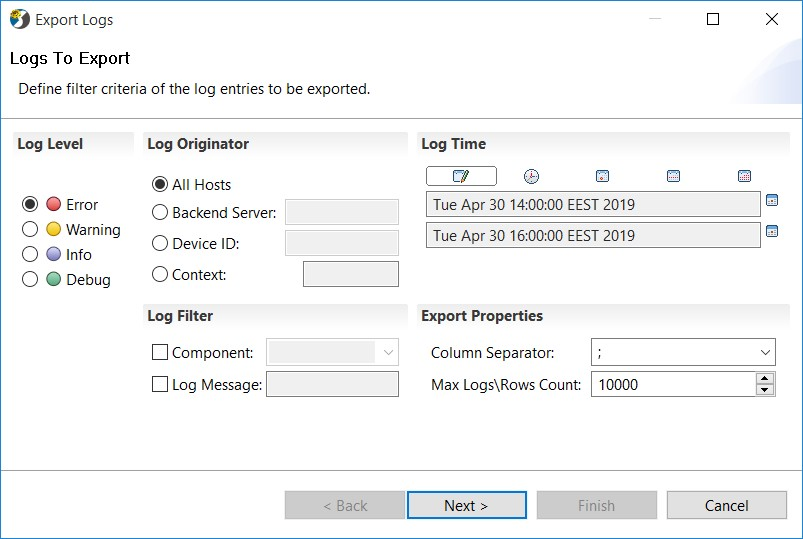
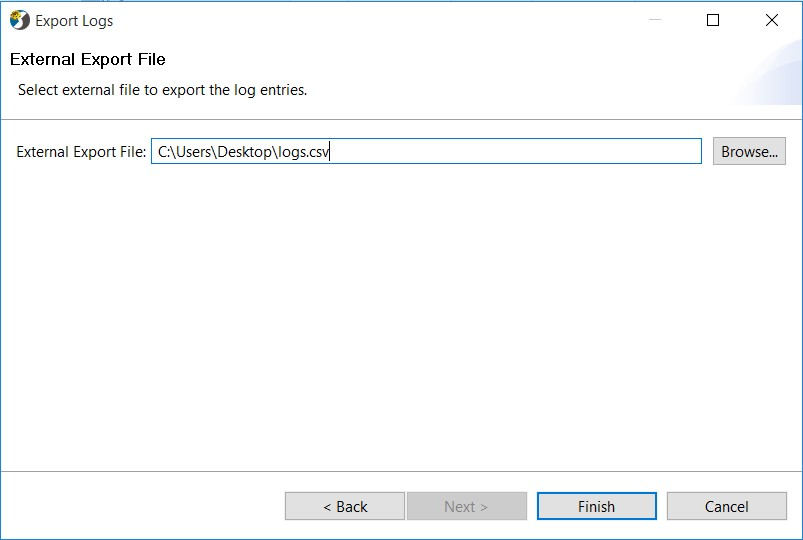
- In the External Export File step, specify the location of the CSV file to save logs to and click Finish.